
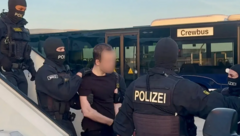
London Hospital Cyber Attack Arrest: Ransomware Operative Detained
The recent London hospital cyber attack arrest of 28-year-old Russian national Vladimir K. marks a watershed moment in international law enforcement. For years, cybercriminals operated under the assumption that keyboard extortion carried financial penalties, not homicide charges. That illusion shattered when German detectives, working alongside Japanese law enforcement and British authorities, intercepted the suspect during an international trip.
The London hospital cyber attack arrest refers to the international detention of 28-year-old Russian national Vladimir K., an alleged core operator of the Qilin ransomware gang. Arrested in Japan and transferred to Frankfurt, he faces charges over devastating hacks against pathology provider Synnovis, which severely disrupted NHS operations and contributed to a patient's death.<\/p>
- Historic Milestone: The arrest marks the first time a cyber attack directly linked to a human fatality has led to potential homicide charges against a ransomware operator.
- International Dragnet: Intelligence agencies intercepted the suspect's vacation plans, leading to his arrest in Japan and subsequent transfer to Frankfurt.
- Devastating NHS Impact: The June 2024 Synnovis attack disrupted over 10,000 appointments, crippled pathology services across London, and contributed to a patient's unexpected death.
- Legal Precedent: British police are evaluating an unlawful killing prosecution, setting a risky new precedent for global cybercrime enforcement.
Extradited from Japan and landed on the tarmac in Frankfurt, Vladimir K. now finds himself at the center of an expanding investigation. What began as a inquiry into extortion against a German logistics provider has evolved into something far more severe: a criminal case exploring whether digital disruption can constitute unlawful killing.
Breakthrough in Cybercrime Enforcement: The London Hospital Cyber Attack Arrest
The arrest highlights an unprecedented evolution in how law enforcement counters global ransomware syndicates. According to intelligence disclosures, Vladimir K. was apprehended by Japanese police upon entering the country for a vacation. His travel itinerary had been secretly monitored by Western law enforcement agencies waiting for him to step outside Russia’s safe borders.
Russian authorities rarely cooperate with Western extradition requests. Consequently, ransomware operators often enjoy near-total domestic immunity provided they avoid domestic targets. However, the decision by Vladimir K. to travel internationally provided the precise leverage law enforcement required.
“When digital attacks knock out core clinical infrastructure, the line between property crime and violent crime vanishes. This arrest proves that geographical boundaries offer temporary shelter, not permanent immunity.”
German federal police initially wanted the 28-year-old for an attack launched in September 2024 against a regional logistics company. In that incident, the perpetrator encrypted critical databases, demanding $160,000 in cryptocurrency. However, investigators soon linked the digital footprint and infrastructure to a far broader pattern of hostility executed by the Qilin ransomware gang.
The Day London’s Blood Line Went Dark
On June 3, 2024, the operational systems of Synnovis—a joint diagnostic partnership between London NHS trusts and German laboratory giant Synlab—went completely dark. Within minutes, pathology services across South London disintegrated.
Hospitals were forced to revert to manual paper processes. Blood transfusions were delayed, elective surgeries were postponed, and emergency ambulances carrying critically ill patients were rerouted across the city. The operational paralysis lasted for weeks, forcing the cancellation of more than 10,000 patient appointments.
- Target: Synnovis (Pathology & Diagnostic Services)
- Impacted Institutions: King’s College Hospital NHS Foundation Trust, Guy’s and St Thomas’ NHS Foundation Trust
- Operational Disruption: Over 10,000 delayed appointments, cancelled surgeries, diverted emergency services
- Extortion Demands: Multi-million dollar ransom demand followed by unauthorized dark net data dumps
A Tragic First: When Digital Extortion Turns Fatal
While economic damage from ransomware is common, the Synnovis breach led to a much darker outcome. One year after the intrusion, King’s College Hospital NHS Foundation Trust confirmed that a patient had died unexpectedly during the service blackout.
An internal patient safety investigation identified several systemic failures caused by the attack, emphasizing that a prolonged delay in obtaining critical blood test results was a primary contributing factor to the death. While medical emergencies are complex, the paralysis of diagnostic infrastructure undeniably compromised patient care.
According to reporting by Reuters, British police are now assessing whether the evidence supports a charge of unlawful killing. If prosecutors proceed down this path, it will represent the world’s first formal homicide prosecution stemming directly from a cyber attack.
The Düsseldorf Precedent
Legal authorities are comparing the London incident to a 2020 ransomware attack on the University Hospital of Düsseldorf. In that instance, a cyber attack forced an emergency patient to be diverted to a facility 20 miles away, where she subsequently died.
German prosecutors launched a negligent homicide investigation against the unknown perpetrators. However, the case ultimately collapsed after forensic medical experts concluded the patient’s underlying condition was so severe that the delay did not definitively cause her death. The legal threshold for causation proved impossible to cross.
In London, however, the facts may yield a different outcome. British investigators are examining whether the direct withholding of pathology results creates a clear, unbroken chain of causation between the hacker’s actions and the patient’s death.
Inside Qilin: The Architecture of a $140M Syndicate
The entity behind the attack, known as Qilin (and occasionally tracked by security researchers as Agenda), represents the modern face of organized cybercrime. Operating on a sophisticated Ransomware-as-a-Service (RaaS) model, the group recruits specialized affiliates to execute network intrusions while providing the underlying encryption software and payment infrastructure.
Since early 2024, Qilin affiliates have targeted more than 4,000 organizations globally, extracting an estimated $140 million (£105 million) from victims spanning municipal governments, educational institutions, and corporate entities. Their victims include major corporations like Japanese beverage giant Asahi, which suffered widespread operational delays following a breach in late 2025.
| Target Entity | Sector | Incident Date | Primary Operational Impact |
|---|---|---|---|
| Synnovis / NHS Trusts | Healthcare / Diagnostics | June 2024 | 10,000+ appointments cancelled; 1 patient fatality link |
| Asahi Group | Manufacturing / Beverage | October 2025 | Supply chain halt and distribution center lockouts |
| German Logistics Firm | Supply Chain | September 2024 | Encrypted systems; $160,000 ransom demand |
| Regional UK Councils | Public Sector | Mid 2024 | Public record leaks and localized system downtime |
Qilin’s tactics are notably aggressive. When victims refuse to pay, the syndicate resorts to double extortion: exfiltrating sensitive internal records and publishing them on public leak sites. Following the Synnovis attack, the group dumped private medical files online after the diagnostic provider refused to meet their ransom demands.
Geopolitical Smokescreens and Criminal Realities
When challenged by journalists during the height of the Synnovis crisis, Qilin operators claimed their actions were politically motivated. They alleged the attack was retaliation against the British government for providing military support to Ukraine.
Cybersecurity analysts and intelligence agencies widely dismissed these claims as performative narrative building. Security analysts at Bloomberg highlighted that criminal groups frequently adopt political talking points to obscure their purely financial motives and confuse public perception.
The Critical Infrastructure Vulnerability
The Synnovis attack exposed critical systemic weaknesses within modern healthcare delivery. Healthcare systems heavily rely on specialized, third-party vendor networks for everything from software maintenance to laboratory diagnostics. This reliance creates extended attack surfaces that are difficult to secure comprehensively.
When a centralized diagnostic partner like Synnovis is compromised, the failure instantly cascades into multiple downstream hospital trusts. The resulting cascade paralyzes emergency rooms, surgical wards, and outpatient clinics simultaneously.
Key Systemic Risks in Healthcare IT Networks
- Legacy Integration Vulnerabilities: Diagnostic equipment often runs on outdated software that cannot support modern security protocols.
- Third-Party Vendor Exposure: Managed service providers often hold high-level access privileges across multiple health networks without sufficient isolation.
- Inadequate Air-Gapping: Medical record databases frequently lack isolated offline backups, leaving them vulnerable to simultaneous encryption.
- Resource Scarcity: Public health organizations regularly struggle to match the compensation rates needed to retain top-tier cybersecurity talent.
The Legal Frontier: Establishing Causation in Cyber Homicide
Prosecuting a cyber attack as an unlawful killing introduces complex legal challenges. To secure a conviction for involuntary manslaughter or negligent homicide, prosecutors must prove key elements beyond a reasonable doubt:
- Duty of Care: Establishing that creating operational risk against a medical provider creates a foreseeable risk to human life.
- Gross Negligence or Malicious Intent: Demonstrating that the defendant knew, or should have known, that disrupting clinical systems would lead to fatal outcomes.
- Direct Causation: Proving that the delay directly caused the fatal outcome, independent of underlying patient health conditions.
Legal scholars note that if British prosecutors succeed in extraditing Vladimir K. to face charges related to the death at King’s College Hospital, it will reshape international cyber law forever. It transforms cybercriminals from mere financial extortionists into potential violent felons subject to life imprisonment.
Hardening the Healthcare Shield
The detention of Vladimir K. offers a critical opportunity for healthcare executives and IT defense teams to overhaul their defense strategies. Catching actors after an attack is vital, but preventing operational downtime remains the primary objective.
Modern defense strategies require moving beyond perimeter security toward strict Zero Trust architectures. Organizations must isolate operational technology (OT) from corporate networks, mandate multi-factor authentication across all remote access points, and perform routine offline backup restorations.
As the legal proceedings in Frankfurt advance and British investigators finalize their files, the message to the international cybercrime ecosystem is clear: the operational disruption of critical health infrastructure is no longer viewed merely as a business loss, but as a potentially fatal crime with worldwide consequences.
<button type="button" onclick="this.parentElement.innerHTML='✓ Thank you, we will refine our analysis!‘” style=”background:#ffffff; border:1px solid #cbd5e1; border-radius:6px; padding:4px 12px; font-size:12px; cursor:pointer; color:#334155;”>👎 No
