
US Immigration Agents Leak Exposes Covert DHS Operations
A staggering US immigration agents leak has laid bare the identities, phone numbers, and internal operational rosters of more than 41,000 federal employees. The compromise strikes directly at the opaque tactical apparatus of the Department of Homeland Security. For years, federal personnel carried out controversial field raids behind tactical balaclavas and unbadged uniforms. Now, a massive repository published online has effectively dismantled that anonymity in one fell swoop.
A massive US immigration agents leak has published unredacted records of over 41,000 Department of Homeland Security personnel. Leaked via a database called Icepick hosted by DDoSecrets, the file details names, phone numbers, undercover operational codenames, and surveillance tools used by ICE and CBP agents.<\/p>
- Massive Scope: Over 41,000 Department of Homeland Security staff records leaked, including 21,000 CBP and 6,600 ICE agents.
- Covert Tactics Unveiled: The breach exposes secret operation names, team leads, and third-party vendor platforms like Cellebrite and Palantir.
- Identity Shield Broken: Tactical masking and hidden badges long relied upon by agents are rendered ineffective by digital dox databases.
- Authentication Breakdown: Hackers allege entry via Okta single sign-on vectors, though Okta claims its systems remain uncompromised.
The breach hit the internet early Wednesday morning. A hacker collective operating under the banner ‘Department of Peace’ teamed up with Swiss cybersecurity researcher maia crimew to publish a indexed database named Icepick. Hosted by transparency site Distributed Denial of Secrets (DDoSecrets), the dump details the granular internal machinery of federal law enforcement. It exposes the names of tactical leaders, secret investigation titles, and private tech tools used to track targets across North America.
Anatomy of the Compromise: Numbers, Agencies, and Vendors
The scale of the breach is staggering. While the dump does not encompass every single staff member within DHS, it captures a deep, operational slice of federal law enforcement. According to technical analysis of the database, federal personnel from nearly every critical division were caught in the harvest.
| Division / Agency | Exposed Personnel Count | Primary Operational Focus Exposed |
|---|---|---|
| Customs and Border Protection (CBP) | 21,000+ | Border surveillance, port-of-entry checks, mobile tactical units |
| Immigration and Customs Enforcement (ICE) | 6,600+ | Interior enforcement, deportation logistics, street-level raids |
| Homeland Security Investigations (HSI) | 3,200+ | Undercover operations, digital forensics, cross-border crime |
| Federal Protective Service & CISA | 10,200+ | Facility defense, critical infrastructure cybersecurity oversight |
Beyond basic personnel records, the repository acts as an blueprint for government surveillance. Dozens of previously undisclosed operation names were exposed alongside the leads who managed them. Furthermore, the dataset outlines active deployments of invasive forensic tools provided by defense contractors, including commercial exploitation software from Reuters reported vendors like Cellebrite and data-mining suites built by Palantir.
“The leak is extraordinary but deceptive in its simplicity as it identifies the officials responsible for overseeing covert and undercover operations, the government’s hunt for leakers, and the failed BlueLeaks investigation—along with key personnel in DHS’s ever-escalating rendition and deportation programs.”
— Emma Best, Co-founder of DDoSecrets
The Identity Shield Flips
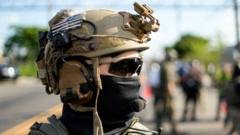
Masks and unmarked uniforms have defined modern immigration raids. Across cities nationwide, agents routinely deploy tactical gaiters, dark sunglasses, and vests stripped of identifying nameplates. While federal regulations technically mandate that personnel disclose their identity during enforcement actions, field execution has been stubbornly anonymous. Congressional leaders have repeatedly criticized this opacity, but field practices remained unchanged—until now.
The digital exposure effectively neutralizes physical facial coverings. By linking phone numbers, workstation assignments, and supervisory structures to specific field locations, activist researchers have bridged the gap between anonymous street agents and official government accountability records.
The Okta Vector and the Identity Debate
How did activists pull off a heist of this magnitude against the world’s largest federal security agency? The Department of Peace pointed directly to single sign-on (SSO) architecture provided by enterprise security provider Okta.
Identity management sits at the absolute center of zero-trust architecture. If an attacker acquires administrative tokens or exploits credential management workflows within an SSO provider, internal database walls crumble quickly. However, Okta moved rapidly to distance its platform from software liability.
“Okta is secure, and we have no evidence our data or systems were compromised,” stated an Okta spokesperson in a statement released shortly after the breach gained global attention. Cybersecurity analysts at Bloomberg suggest the breach likely stemmed from compromised high-level administrative credentials or third-party API misconfigurations rather than a core zero-day vulnerability in Okta’s cloud infrastructure.
A Escalating Campaign of Targeted Intrusions
This incident is not an isolated event. It represents the latest wave in a relentless cycle of intrusions targeting US federal law enforcement institutions:
- FBI Personnel Breach: Just weeks prior, hacker group ShinyHunters infiltrated FBI communications channels, exfiltrating personal data on thousands of agents.
- Federal Election Commission Downtime: The FEC saw its public donation systems knocked offline following a sustained cyber intrusion.
- The BlueLeaks Precedent: In 2020, DDoSecrets published hundreds of gigabytes of sensitive local police intelligence files, fundamentally altering state-level cyber risk assessments.
The political rhetoric surrounding the hack is equally intense. Activists framed the dump as direct retaliation against expanding enforcement mandates under Homeland Security leadership. When asked about their motives, spokesperson networks cited aggressive public statements made by leadership regarding aggressive deportation quotas.
Political Fallout and Cyber Implications
The breach arrives amidst a backdrop of rising civil tension and drastic policy shifts. According to data tracked by the Migration Policy Institute, federal agencies have executed nearly one million deportations over recent cycles. Significantly, more than 70 percent of individuals impacted carried no prior criminal record. High-profile, fatal enforcement mistakes in suburban neighborhoods have sparked national outrage, transforming immigration policy into a political powder keg.
Now, federal law enforcement faces a double-barreled crisis: physical security vulnerabilities in the field coupled with an absolute collapse of digital perimeter defenses. Industry experts emphasize that the long-term threat to DHS staff is not merely spam or phone pranks—it is targeted spear-phishing, social engineering, and potential physical doxxing.
When deep operational logs spill into the public domain, repairing the damage takes years. Codenames must be retired. Software contracts require auditing. Agents working undercover must be reassigned immediately to avert fatal compromise. The breach proves that in an era of ubiquitous digital logging, true state anonymity may no longer exist.
<button type="button" onclick="this.parentElement.innerHTML='✓ Thank you, we will refine our analysis!‘” style=”background:#ffffff; border:1px solid #cbd5e1; border-radius:6px; padding:4px 12px; font-size:12px; cursor:pointer; color:#334155;”>👎 No
Latest Analytical Follow-up: For continuous developments on this subject, read our full investigation on Musk Putin Satellite Talks Highlight New Orbital Diplomacy.
Latest Analytical Follow-up: For continuous developments on this subject, read our full investigation on Microsoft Profits Soar to $36.6B Amid Massive AI Spending Pivot.
