
Smart Device Cyber Vulnerabilities: Beyond Supermarket Hacks
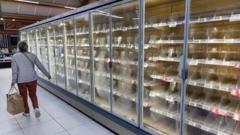
When digital intrusions breach physical space, the cost isn’t just stolen data—it’s ruined inventory, paralyzed logistics, and melted cooling systems. The recent widespread compromise of commercial refrigeration units across seven European countries highlighted how critical operational systems remain exposed to growing smart device cyber vulnerabilities. Cold chains collapsed overnight. Store managers scrambled to salvage produce. Upstream logistics backed up for miles.
Smart device cyber vulnerabilities occur when internet-connected hardware—ranging from commercial supermarket freezers to domestic smart appliances and industrial controls—contains unpatched software flaws, default credentials, or unencrypted data flows. Malicious actors exploit these exposed interfaces to remotely alter physical operations, disrupt supply chains, or deploy ransomware across critical infrastructure.<\/p>
- Key Insight 1: Recent cyber incidents targeting European supermarket freezers demonstrate how operational technology can be weaponized to destroy physical inventory.
- Key Insight 2: Security researchers uncovered more than 800 exposed building-control and refrigeration interfaces connected to the public internet in the UK alone.
- Key Insight 3: Legitimate maintenance features, such as remote defrost cycles, become destructive vectors when hijacked by malicious actors.
- Key Insight 4: Regulatory frameworks like the UK's PSTI Act establish mandatory security baselines, yet legacy industrial hardware remains exposed worldwide.
This was not an isolated system glitch. It was a stark warning of what happens when embedded hardware meets internet connectivity without adequate defense engineering. The incident has sent shockwaves through retail boardrooms and industrial facilities globally, forcing a long-overdue reckoning with the invisible risk vectors embedded in modern appliances.
The Chilling Reality of Operational Cyber Threats
For years, enterprise risk assessments focused almost entirely on corporate servers, cloud databases, and employee laptops. Operational Technology (OT)—the hardware and software that monitors and controls physical devices—was treated as an isolated island. That boundary has effectively vanished. Contemporary enterprise environments rely on internet-connected hardware to optimize energy consumption, schedule predictive maintenance, and monitor operations in real time. Yet, every online interface creates an entry point.
When unauthorized actors gain control of these endpoints, legitimate maintenance actions become vectors for physical disruption. Consider the mechanics of commercial refrigeration. Modern chillers rely on automated defrost cycles to prevent ice buildup on evaporator coils. Under normal operating conditions, these cycles engage briefly and predictably. However, if a malicious entity overrides these controls and forces an extended defrost cycle, ambient temperatures spike rapidly.
“Once an attacker can operate those controls, legitimate functions such as defrosting become tools for disruption,” explains Tom Hegel, a threat researcher at security firm SentinelOne. “Changing a setting can destroy physical stock, not just interrupt a computer system.”
The operational consequences are severe. A single grocery retail chain can lose millions of euros in fresh produce within hours if storage conditions breach regulatory safety limits. Similar vulnerability patterns played out during previous supply chain disruptions. When major UK grocery networks like M&S and the Co-op encountered severe ransomware incidents, the primary impact manifested on physical shop shelves. Logistics networks lost real-time tracking, distribution centers stalled, and consumers were greeted by empty aisles. The European freezer incidents demonstrate how direct manipulation of hardware exacerbates these vulnerabilities without requiring full system encryption.
Mapping the Attack Surface: From Shop Floors to Domestic Kitchens
Is the threat limited to multinational commercial chains, or should consumers worry about their connected home appliances? To understand the scope, one must analyze how smart hardware connects to public and private networks. Internet-connected appliances—whether an industrial freezer array or a household smart refrigerator—depend on firmware interfaces, mobile application programming interfaces (APIs), and persistent cloud connections.
Researchers have identified security oversights across consumer hardware for over a decade. Back in 2015, cybersecurity analysts demonstrated how a flaw in a Samsung smart refrigerator allowed man-in-the-middle traffic interception, exposing user credentials. While domestic hardware can theoretically be exploited, current threat intelligence indicates zero evidence that home appliances are being targeted in the ongoing wave of supermarket cyber attacks.
The risk profiles for consumer and enterprise hardware differ substantially in scale and intent:
- Enterprise Hardware: High physical impact, centralized control systems, complex supply chain integration, high potential for financial extortion or state-sponsored sabotage.
- Consumer Hardware: Low individual physical impact, localized network exposure, primary risk centered on privacy leaks or recruitment into distributed denial-of-service (DDoS) botnets.
Former Chief Executive of the UK National Cyber Security Centre (NCSC), Ciaran Martin, emphasizes that device security cannot remain an afterthought for hardware manufacturers. “There’s a lot more that we need to demand of big tech to give us safer devices and products in the first place,” Martin noted, adding that while consumer hygiene like multi-factor authentication (MFA) and routine firmware updates help, structural security must originate at the engineering level.
Unshielded Interfaces: Over 800 British Retail Systems Exposed
Why are industrial appliances so easily targeted? The answer often lies in basic network architecture errors. Investigations conducted by UK Cyber Defence revealed that over 800 refrigeration and building-control interfaces belonging to British entities remain directly reachable over the public internet.
An exposed interface does not automatically equal a compromised system. However, it exposes the control panel to brute-force credential attempts, known software exploit kits, and unpatched zero-day vulnerabilities. Many of these industrial management portals were originally designed for isolated internal networks. When third-party vendors retrofitted them with remote access capabilities to allow off-site technicians to diagnose issues, essential security layers were frequently omitted.
According to coverage by Reuters on global supply chain vulnerabilities, third-party vendor access remains one of the primary entry channels for threat actors attempting to penetrate enterprise networks. This structural disconnect highlights a critical organizational question: where does operational accountability end and cybersecurity oversight begin?
Tom Hegel points directly to this ambiguity. “The question retailers need to answer is who owns the security of that equipment, not just who repairs it,” Hegel stressed. When maintenance contracted to external suppliers lacks strict oversight, security controls drop precipitously.
Sector Risk Comparison: Physical Vulnerabilities in Connected Hardware
To visualize how internet-connected hardware vulnerabilities manifest across different industries, consider the following comparative matrix detailing target hardware, exposure routes, and potential impacts.
| Industry Sector | Target Hardware | Primary Attack Vector | Operational Impact Level | Mitigating Framework |
|---|---|---|---|---|
| Commercial Retail | Smart Freezers & Chillers | Exposed Web Portals / Weak Vendor Passwords | High (Stock Destruction, Inventory Spoilage) | Network Micro-segmentation & MFA |
| Public Utilities | Water Treatment Valves & Pumps | Legacy OT / Unencrypted Cellular Modems | Catastrophic (Service Disruption, Public Hazard) | NIST CSF & Air-Gapped Networks |
| Automotive & Transport | Vehicle Telematics & Fleet Systems | Cellular Gateway & CAN Bus Exploits | High (Safety Risks, Fleet Immobilization) | Automotive ISO/SAE 21434 Standard |
| Manufacturing | Robotic Assembly & CNC Machines | Unpatched Firmware & Compromised Maintenance Tools | High (Production Line Halts, Equipment Damage) | IEC 62443 Industrial Security Standard |
| Consumer Smart Home | Smart Fridges, Thermostats, HVAC | Default Passwords & Unauthenticated APIs | Low to Medium (Data Privacy, Botnet Recruitment) | UK PSTI Act & EU Cyber Resilience Act |
Understanding Smart Device Cyber Vulnerabilities in Industrial Hardware
The risk profile extends far beyond retail store aisles. The expansion of operational technology hacking poses systemic threats to manufacturing plants, water distribution networks, and municipal transport infrastructure. Industrial facilities heavily rely on cellular telemetry modems to send performance metrics to central dashboards. While these modems allow engineers to troubleshoot issues from hundreds of miles away, they also expose physical machinery to the open web.
Cybersecurity expert Ken Munro highlights how historical hardware vulnerabilities led to dramatic safety reforms in other sectors. In 2015, security researchers famously demonstrated the remote hijack of a Jeep Cherokee via its internet-connected infotainment platform. The researchers killed the engine and disabled the brakes while the vehicle was moving on a highway. That landmark experiment forced the automotive industry to fundamentally re-engineer internal vehicle communication buses.
“Fortunately, the vehicle industry woke up to this and fixed the problem,” Munro observed, noting that while major utility operators in Western nations generally secure their connections, smaller regional operations lag behind. “My biggest concern is smaller, poorly funded utility companies which may still be relying on older, vulnerable equipment.”
Without baseline protections, virtually any machinery connected to an unsegmented network remains open to disruption. Olivier Daloy, a cybersecurity specialist at Zscaler, points out that unmanaged edge endpoints create unprecedented entry points. Whether an attacker targets a car assembly line, an electrical distribution node, or a commercial cooling plant, the underlying attack vector relies on the same systemic flaw: unauthenticated commands sent to physical actuators.
Financial news outlets including Bloomberg have increasingly underscored how capital expenditure in industrial automation often neglects long-term software maintenance, leaving legacy control hardware vulnerable for decades.
Regulatory Mandates and the Push for Hardware Security Baselines
In response to growing supply chain risks, governments are moving from voluntary guidelines to mandatory enforcement. Legislative efforts aim to force hardware developers and commercial operators to build resilience directly into product architectures.
A major milestone arrived with the implementation of the UK’s Product Security and Telecommunications Infrastructure (PSTI) Act. The legislation prohibits manufacturers from shipping smart hardware with generic, default passwords like “admin” or “123456”. Furthermore, it mandates that companies maintain transparent vulnerability disclosure policies and explicitly state the minimum time frame during which a device will receive security updates.
Key Provisions of Modern Connected Hardware Standards
- Elimination of Default Credentials: Every internet-connected hardware device must ship with a unique factory password or require a mandatory password update upon initial configuration.
- Mandatory Vulnerability Reporting: Manufacturers must provide public contact points for security researchers to report flaws promptly.
- Transparent Lifecycle Support: Retailers and manufacturers must clearly inform buyers how long a product will receive active security patches prior to purchase.
- Supply Chain Auditability: Commercial organizations are encouraged to maintain a Software Bill of Materials (SBOM) for all operational technology running on critical networks.
Helen Dickinson, Chief Executive of the British Retail Consortium, highlighted that market operators are prioritizing cyber resilience. Retailers are actively collaborating with national intelligence authorities to exchange threat indicators and harden exposed interfaces. However, regulatory frameworks like the PSTI Act primarily govern new consumer hardware. Resolving the millions of legacy industrial controllers already deployed across global infrastructure remains a colossal operational challenge.
Closing the Gaps: Engineering Resilient Connected Ecosystems
Mitigating industrial IoT security risks demands a complete shift in operational philosophy. IT teams and facility management departments can no longer operate in silos. Equipment security must cover physical repairs as well as digital hardening.
Organizations deploying internet-connected hardware must implement a multi-layered defense model:
- Network Segmentation: Isolate all operational technology, environmental controls, and industrial appliances on dedicated Virtual Local Area Networks (VLANs). Ensure hardware control panels are never accessible from the public internet.
- Zero Trust Access Policies: Require strict multi-factor authentication and encrypted VPN connections for any remote maintenance or diagnostic sessions.
- Continuous Asset Discovery: Utilize specialized scanning tools to monitor external IP ranges for exposed building-control interfaces and unauthorized IoT devices.
- Vendor Security Governance: Mandate strict cybersecurity compliance clauses in all third-party maintenance contracts, clearly establishing legal accountability for device patching.
The supermarket freezer breaches proved that digital attacks produce tangible, real-world fallout. As physical machinery becomes increasingly reliant on cloud connectivity, the line between software security and physical safety has evaporated. Defending connected infrastructure requires continuous vigilance, strict regulatory compliance, and a zero-trust approach to hardware management.
<button type="button" onclick="this.parentElement.innerHTML='✓ Thank you, we will refine our analysis!‘” style=”background:#ffffff; border:1px solid #cbd5e1; border-radius:6px; padding:4px 12px; font-size:12px; cursor:pointer; color:#334155;”>👎 No
Latest Analytical Follow-up: For continuous developments on this subject, read our full investigation on Foldable iPhone Supply Uncertainty as Apple Duo Sells Out.
